VM
PM Tools
SecOps
How to Evaluate Vulnerability & Patch Management Software: A Practical POC Checklist

Ashwani Paliwal
November 3, 2026

Choosing vulnerability and patch management software is an important investment for any organization's IT and security operations. The right platform should help teams discover assets, identify security weaknesses, prioritize risks, deploy patches safely, and verify remediation.
However, comparing vendors can be challenging. Most solutions advertise similar features, including vulnerability scanning, automated patching, risk prioritization, compliance reporting, and centralized management. The real difference becomes clear when these capabilities are tested against your infrastructure.
This guide outlines 16 practical tests that IT managers, infrastructure teams, and security professionals can use to evaluate vulnerability and patch management platforms during a proof of concept (POC). Each test includes the key evaluation criteria, measurable outcomes, and evidence to request from vendors.
A vulnerability management platform must identify the assets within your environment to provide reliable security visibility.
What to evaluate:
How to test: Compare discovered assets against your existing inventory. Introduce additional test systems during the POC to assess discovery speed and accuracy.
Measure:
Evidence: Exported inventory, discovery timestamps, classification reports, and supported discovery methods.
The platform must accurately identify known vulnerabilities without generating excessive false positives or overlooking security weaknesses.
What to evaluate:
How to test: Scan systems containing known vulnerable software versions alongside systems that have already received the relevant security updates. Compare findings against an independently verified test inventory.
Measure:
Evidence: CVE-level assessment reports, detection records, false-positive investigation results, and intelligence update history.
Operating system compatibility determines whether a platform can manage your existing infrastructure without requiring additional patching tools.
What to evaluate:
How to test: Select representative systems running the operating systems used in your organization. Perform inventory scans and deploy an approved security update on each supported configuration.
Measure:
Evidence: Official OS compatibility matrix, test results, deployment logs, and documented limitations.
Deployment architecture affects administrative effort, endpoint resource consumption, and ongoing maintenance.
What to evaluate:
How to test: Assess representative Windows and Linux systems across different network segments without installing persistent agents. Where applicable, compare the results with an agent-based deployment.
Measure:
Evidence: Architecture diagram, network requirements, credential management documentation, component inventory, and resource utilization logs.
Operating system updates alone cannot address vulnerabilities introduced by outdated applications.
What to evaluate:
How to test: Install outdated versions of commonly used applications, such as Google Chrome, Mozilla Firefox, Adobe Acrobat Reader, and 7-Zip. Identify missing updates and deploy applicable patches.
Measure:
Evidence: Supported application catalog, version inventory, deployment logs, before-and-after version reports, and coverage limitations.
Prioritizing vulnerabilities based only on CVSS severity may not reflect the actual security risk to an organization.
What to evaluate:
How to test: Evaluate vulnerabilities with different risk characteristics, including high-CVSS/low-EPSS findings, medium-CVSS/high-EPSS findings, KEV-listed vulnerabilities, and issues affecting critical or internet-facing assets.
Compare the results against predefined organizational risk criteria.
Measure:
Evidence: Risk prioritization reports, CVSS and EPSS values, KEV records, scoring methodology, and asset criticality information.
Identifying vulnerabilities is only the first step. The platform should help administrators determine which updates can remediate them.
What to evaluate:
How to test: Select known vulnerabilities and ask the platform to identify the corresponding remediation updates. Validate the recommendations against vendor advisories and affected software versions.
Measure:
Evidence: Vulnerability-to-patch mapping reports, patch metadata, applicability records, and unsupported vulnerability details.
Patch deployment should be reliable, controlled, and aligned with business maintenance requirements.
What to evaluate:
How to test: Deploy an approved security update to selected test systems in multiple rollout groups. Evaluate the approval process, scheduling, deployment progress, and expansion to subsequent groups.
Measure:
Evidence: Deployment logs, approval records, scheduling configuration, reboot reports, and rollout status.
A patch can introduce compatibility issues or affect system stability. Recovery capabilities are therefore important when evaluating patch management software.
What to evaluate:
How to test: Deploy an update with a documented uninstall or rollback procedure on a test system. Simulate a compatibility issue and execute the supported recovery process.
Measure:
Evidence: Rollback logs, recovery documentation, before-and-after system states, and supported rollback scenarios.
A successful installation does not necessarily mean that the vulnerability has been eliminated. Independent verification is essential.
What to evaluate:
How to test: Patch systems with known vulnerabilities and run another vulnerability assessment. Include a system with a pending reboot to check whether the platform accurately reflects its remediation status.
Measure:
Evidence: Before-and-after vulnerability reports, installation records, reassessment results, reboot status, and remediation timestamps.
Patch failures are inevitable in complex IT environments. The platform should help administrators identify their causes and take corrective action.
What to evaluate:
How to test: Introduce controlled failure scenarios, such as insufficient disk space, unavailable network connectivity, missing permissions, unsupported patches, and pending reboots. Observe how the platform detects and reports each failure.
Measure:
Evidence: Failure logs, error codes, retry history, alerts, and troubleshooting recommendations.
Reporting should demonstrate what was discovered, which remediation actions were performed, and whether security risks were successfully addressed.
What to evaluate:
How to test: Generate reports before and after a patch deployment exercise. Verify that they capture affected assets, vulnerabilities, assigned patches, deployment status, and final remediation status.
Measure:
Evidence: Sample vulnerability and compliance reports, remediation history, exported CSV/PDF files, and audit logs.
Vulnerability and patch management platforms handle sensitive infrastructure information and privileged operations. Access must be controlled appropriately.
What to evaluate:
How to test: Create security analyst, patch administrator, and auditor accounts. Attempt authorized and restricted operations using each account.
Measure:
Evidence: Role-permission matrix, RBAC configuration, MFA documentation, audit log exports, and identity provider integration details.
Scanning and patch deployment can affect network performance and endpoint resources, particularly in organizations with remote employees and distributed offices.
What to evaluate:
How to test: Run vulnerability assessments and patch deployments across representative systems while monitoring network traffic, CPU, and memory. Repeat with different deployment concurrency levels.
Measure:
Evidence: Network utilization reports, resource consumption logs, deployment benchmarks, and caching architecture documentation.
A platform should support the organization's current infrastructure and anticipated growth without creating excessive operational overhead.
What to evaluate:
How to test: Evaluate performance using a representative sample of your infrastructure. Ask the vendor to demonstrate larger-scale workloads through documented benchmarks or a representative load test, clearly identifying the test conditions.
Measure:
Evidence: Scalability benchmarks, reference architecture, supported asset limits, infrastructure sizing, and customer references with comparable environments.
The platform should integrate with existing IT and security tools to reduce manual work and streamline remediation.
What to evaluate:
How to test: Connect an available ITSM or ticketing platform. Generate a remediation ticket from a critical vulnerability, deploy the relevant patch, and verify whether the ticket reflects the final remediation status.
Measure:
Evidence: Integration and API documentation, workflow configuration, ticket records, synchronization logs, and error-handling details.
Testing individual capabilities is useful, but organizations also need a consistent method to compare vendors.
Use a 0–5 scoring scale for each test:

Not every capability has the same business importance. Assign weights according to the following example and adjust them based on your organization's priorities.
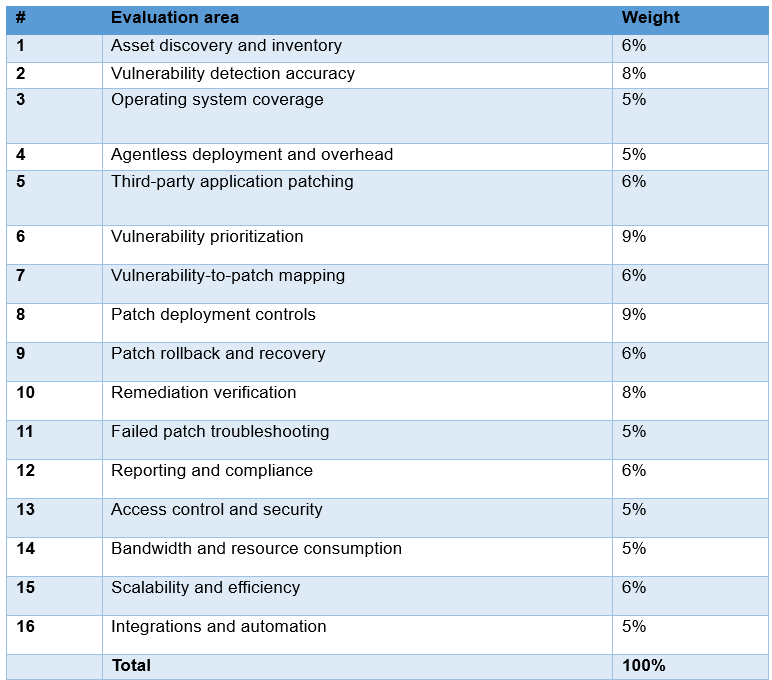
Weighted Score = (Individual Test Score ÷ 5) × Assigned Weight
Add all weighted scores to calculate the vendor's overall POC score.
For example, if a vendor scores 4 out of 5 on a capability weighted at 10%, its contribution to the overall score is 8 percentage points.
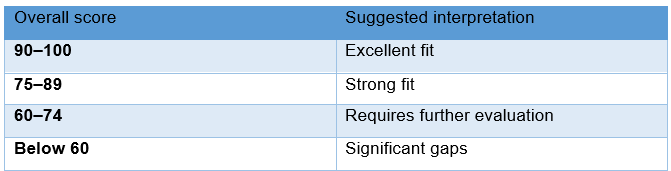
These ranges are indicative, not universal acceptance thresholds. Organizations should establish their own minimum requirements and identify critical capabilities that cannot be compensated for by higher scores elsewhere.
SecOps Solution provides an integrated approach to vulnerability and patch management, helping organizations identify vulnerabilities, prioritize risks, and manage remediation across their infrastructure.
During a POC, IT and security teams can evaluate capabilities such as:
Evaluate each capability against your own requirements, supported configurations, and predefined acceptance criteria.
Choosing vulnerability and patch management software is about finding a platform that reduces security exposure without introducing unnecessary operational complexity.
A feature list alone cannot demonstrate whether a solution will work effectively in your environment. A structured POC should validate the complete vulnerability remediation lifecycle:
Discover → Assess → Prioritize → Patch → Verify → Report
Use measurable results, documented evidence, and weighted scoring to compare vendors objectively. Most importantly, select a solution based on demonstrated capabilities rather than marketing claims.
SecOps Solution is an agent-based and agentless patch and vulnerability management platform that helps organizations quickly remediate security risks across operating systems and third-party applications, both on-prem and remote.
Contact us to learn more.